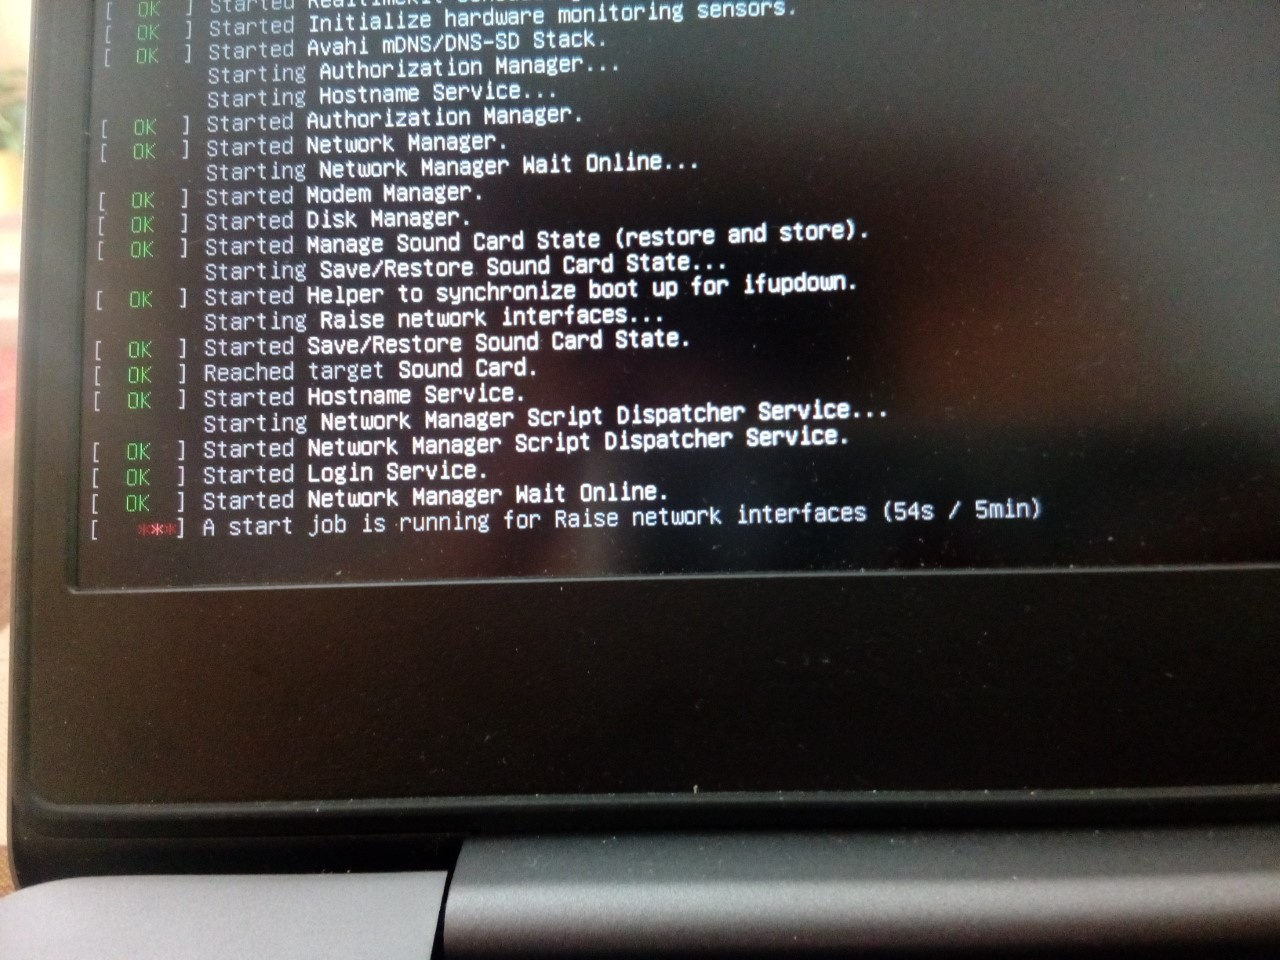
Bonjour,
J’ai upgrade pour la version buster. Suite au redémarrage mon périphérique wifi avait le statu « non prêt ». Je l’ai ensuite redémarré et il à fonctionné correctement. J’ai ensuite installé openvpn et networtk-manager-openvpn. (mon but étant d’utiliser Cyberghost). J’ai redémarré et la même problème que lors du premier démarrage. J’ai donc désinstallé ce que je venais d’installer et ça ne marche pas.
Voila ce qui apparaît quand je démarre:
Tu as surement un script dans /etc/NetworkManager/dispatcher.d qui est resté suite à ton install, qui met le boxon.
Regardes dans le dossier et supprime (ou enlève la permission d’exécution - poste ici avant pour avoir un avis préalable) ce qui pourrait ressembler au script qui bloque ton démarrage.
Le problème aparait de temps en temps et je suis obligé de redémarré jusqu’à ce que le boot ce passe bien.
Dans /etc/NetworkManager/dispatcher.d j’ai les dossier suivants : no-wait.d pre-down.d pre-up.d
et un fichier texte :
#!/bin/sh -e
# Script to dispatch NetworkManager events
#
# Runs ifupdown scripts when NetworkManager fiddles with interfaces.
# See NetworkManager(8) for further documentation of the dispatcher events.

# We do not handle connectivity-change events in ifupdown so simply exit at
# this point
if [ "$2" = "connectivity-change" ]; then
    exit 0;
fi

if [ -z "$1" ]; then
    echo "$0: called with no interface" 1>&2
    exit 1;
fi

if [ -n "$IP4_NUM_ADDRESSES" ] && [ "$IP4_NUM_ADDRESSES" -gt 0 ]; then
   ADDRESS_FAMILIES="$ADDRESS_FAMILIES inet"
fi
if [ -n "$IP6_NUM_ADDRESSES" ] && [ "$IP6_NUM_ADDRESSES" -gt 0 ]; then
   ADDRESS_FAMILIES="$ADDRESS_FAMILIES inet6"
fi

# If we have a VPN connection ignore the underlying IP address(es)
if [ "$2" = "vpn-up" ] || [ "$2" = "vpn-down" ]; then
   ADDRESS_FAMILIES=""
fi

if [ -n "$VPN_IP4_NUM_ADDRESSES" ] && [ "$VPN_IP4_NUM_ADDRESSES" -gt 0 ]; then
   ADDRESS_FAMILIES="$ADDRESS_FAMILIES inet"
fi
if [ -n "$VPN_IP6_NUM_ADDRESSES" ] && [ "$VPN_IP6_NUM_ADDRESSES" -gt 0 ]; then
   ADDRESS_FAMILIES="$ADDRESS_FAMILIES inet6"
fi

# We're probably bringing the interface down.
[ -n "$ADDRESS_FAMILIES" ] || ADDRESS_FAMILIES="inet"

# Fake ifupdown environment
export IFACE="$1"
export LOGICAL="$1"
export METHOD="NetworkManager"
export VERBOSITY="0"

for i in $ADDRESS_FAMILIES; do

    export ADDRFAM="$i"

    # Run the right scripts
    case "$2" in
        up|vpn-up)
            export MODE="start"
            export PHASE="post-up"
            run-parts /etc/network/if-up.d
            ;;
        down|vpn-down)
            export MODE="stop"
            export PHASE="post-down"
            run-parts /etc/network/if-post-down.d
            ;;
# pre-up/pre-down not implemented. See
# https://bugzilla.gnome.org/show_bug.cgi?id=387832
#        pre-up)
#            export MODE="start"
#            export PHASE="pre-up"
#            run-parts /etc/network/if-pre-up.d
#            ;;
#        pre-down)
#            export MODE="stop"
#            export PHASE="pre-down"
#            run-parts /etc/network/if-down.d
#            ;;
        hostname|dhcp4-change|dhcp6-change)
            # Do nothing
            ;;
        *)
            echo "$0: called with unknown action \`$2'" 1>&2
            exit 1
            ;;
    esac
done